
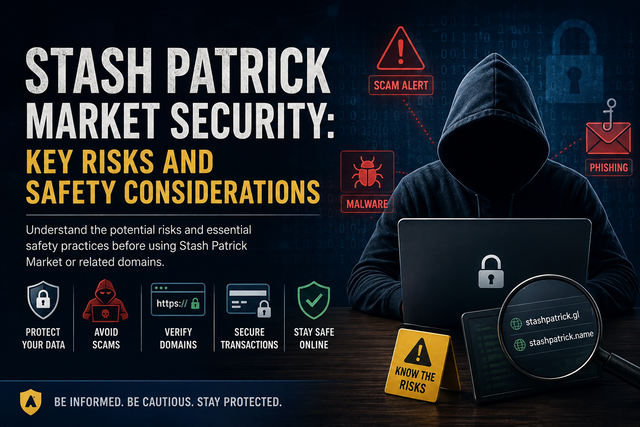
The internet has become an essential part of everyday life, giving people access to websites, online services, marketplaces, communities, and financial platforms within seconds. However, convenience also creates security challenges. stash patrick Not every website is transparent about its ownership, data practices, or security standards. Before interacting with an unfamiliar website associated with a name such as Stash Patrick, users should take time to perform basic security checks.
Website security is about more than whether a page looks professional. A convincing design can be copied, security claims can stashpatrick.cc be exaggerated, and unfamiliar websites may collect information that visitors do not fully understand. Learning how to evaluate an online destination can help users reduce unnecessary risks.
1. Check the Website Address
The first security check is the website’s address. Users should carefully examine the domain name before entering information or clicking links.
Look for unusual spelling, unexpected characters, misleading subdomains, and addresses that resemble established services. Attackers sometimes create domains designed to look similar to legitimate websites.
Users should also check whether the browser connects through HTTPS. HTTPS encrypts communication between a browser and a website, helping protect information while it is transmitted. However, HTTPS alone does not prove that a website is legitimate. Suspicious websites can also use encrypted connections.
Therefore, the domain and HTTPS status should be considered together with other evidence.
2. Understand the Website’s Purpose
Before creating an account or interacting with an unfamiliar service, users should understand exactly what the website claims to do.
A website should provide enough information for visitors to understand its purpose, intended audience, and services. If the purpose is unclear or the website makes unusually broad claims without supporting details, additional research is appropriate.
Users should avoid trusting a service simply because its pages contain professional graphics, testimonials, or promotional language. Presentation is not the same thing as verification.
3. Research Independent Sources
One of the strongest basic security practices is researching a website outside the website itself.
Independent sources may include cybersecurity publications, consumer-protection organizations, established technology publications, academic research, and other reputable resources.
Search for the website’s domain and look for information concerning its reputation, ownership, security history, or reported problems.
Users should also distinguish between independent evidence and promotional material. A website’s own testimonials or advertisements are not the same as third-party verification.
If multiple credible sources provide consistent information, users can make a more informed assessment.
4. Review Privacy Information
Privacy should be a major consideration before providing personal information.
Users should examine whether the website explains what information it collects, why that information is needed, how long it may be retained, and whether it may be shared with other organizations.
A privacy policy should be understandable enough for an ordinary visitor to determine how personal information is handled.
If a website asks for sensitive information without clearly explaining why it is necessary, users should reconsider whether registration is appropriate.
5. Examine Account Requirements
Account creation is another area where users should apply caution.
An unfamiliar website should not receive passwords that are already used for email, banking, social media, or other important accounts. Every important service should ideally have a unique password.
Password reuse can create a serious security problem. If credentials are exposed through one service, attackers may attempt to use the same credentials elsewhere.
Multi-factor authentication can provide additional protection when it is available. Users should also keep recovery information secure and never share authentication codes with other people.
6. Be Careful With Downloads
Downloads deserve particular attention when visiting unfamiliar websites.
A site may encourage visitors to install software, browser extensions, applications, or other files. Users should not install programs simply because a webpage claims that they are required.
Software should preferably be downloaded from official developer websites or established application stores. Files from unknown sources can potentially contain malware, spyware, ransomware, or unwanted programs.
If an unfamiliar site asks visitors to disable security software before downloading something, that should be treated as a significant warning sign.
7. Watch for Phishing Indicators
Phishing is one of the most common techniques used to steal online credentials and personal information.
Warning signs may include urgent requests, unexpected account alerts, suspicious login pages, unusual payment requests, and messages that pressure users into acting immediately.
Users should avoid clicking unexpected links in emails, messages, or advertisements. Instead, they can manually navigate to a known official website using a trusted address.
A legitimate organization should not normally require users to reveal passwords or authentication codes through an unsolicited message.
8. Check Financial Requests Carefully
Extra caution is necessary when a website requests financial information.
Users should understand why a payment is being requested, who is receiving it, and what protections are available. Unusual payment methods, unexplained fees, pressure to act quickly, or requests for sensitive financial credentials should receive additional scrutiny.
Users should never provide banking passwords, one-time authentication codes, or similar credentials to an unfamiliar website.
For legitimate purchases and services, users should verify the business independently and use established payment channels where possible.
9. Pay Attention to Browser Warnings
Modern browsers include security features designed to warn users about potentially dangerous websites, downloads, and deceptive pages.
These warnings should not be ignored automatically.
A browser warning does not necessarily provide a complete explanation of a website’s history, but it is an important signal that further investigation may be appropriate.
Users can also keep their browsers, operating systems, and security software updated. Security updates frequently address vulnerabilities that could otherwise be exploited by malicious websites or software.
10. Consider the Website’s Transparency
Transparency is an important indicator when evaluating an unfamiliar online service.
Users should look for information about the organization responsible for the website, contact methods, terms of service, privacy practices, and other relevant policies.
A lack of basic information does not automatically prove that a website is dangerous. However, limited transparency makes it harder for users to determine who is responsible for the service and how problems can be addressed.
Websites requesting sensitive information deserve especially careful examination.
11. Do Not Use Real Credentials for Testing
Users sometimes believe they can determine whether an unfamiliar website is legitimate by creating an account and seeing what happens.
This approach can create unnecessary risk.
There is no need to provide a real email password, banking credential, payment-card information, identity document, or authentication code merely to test a website.
Research can usually be performed through publicly available information. If users cannot evaluate a service without exposing sensitive information, they should consider whether continuing is worthwhile.
12. Know What to Do After a Suspicious Visit
If someone has already visited an unfamiliar website, there is no reason to panic. Simply opening a webpage does not automatically mean that an account or device has been compromised.
However, users should consider what they did while visiting.
If they entered a password, changing that password through the legitimate service may be appropriate, especially if it was reused elsewhere. If financial information was submitted, contacting the relevant financial institution through an official channel may be appropriate.
If a suspicious file was downloaded, users should avoid opening it and use reputable security software to examine the device.
Building Safer Online Habits
Website security is most effective when it becomes a routine habit. Users should verify unfamiliar domains, use unique passwords, enable multi-factor authentication, install software updates, and avoid suspicious downloads.
They should also question websites that create unnecessary urgency or request sensitive information without a clear explanation.
The goal is not to assume that every unfamiliar website is dangerous. Instead, users should recognize that unfamiliar services require verification before trust is established.
Conclusion
A Stash Patrick website guide should ultimately focus on practical security awareness rather than assumptions about a particular domain. Before trusting an unfamiliar website, users should check its address, research independent sources, review privacy practices, protect account credentials, avoid questionable downloads, and carefully evaluate financial requests.
These checks are useful across the entire internet. Whether visiting a new marketplace, service provider, community, or information website, users can reduce their exposure to scams and security threats by verifying information before taking action.
Good cybersecurity does not require advanced technical skills. It starts with simple habits: pause, inspect, verify, and protect sensitive information. When reliable information remains unavailable, delaying interaction is often safer than taking unnecessary risks.